Dallas CISO Community
Executive Summit
November 4, 2026 | The Westin Irving Convention Center at Las Colinas
November 4, 2026
The Westin Irving Convention Center at Las Colinas
Join fellow CISOs for a day of peer connections, peer perspectives and Gartner insights
The Gartner Dallas CISO Community Executive Summit is the community’s signature event, bringing together CISOs for a full day of immersive, peer-driven discussions and curated networking. Connect with peers who share similar priorities, exchange real-world experiences and gain data-driven insights from Gartner analysts. Walk away with practical solutions, validated strategies and valuable connections, giving you greater confidence to lead through change.
Participate in discussions on the most critical issues impacting CISOs today:
Advancing GenAI Capabilities with Secure and Accountable Oversight
Streamlining Tools and Processes to Improve User Experience, Productivity, and Business Value
Integrating Cyber Resilience into Core Business Strategy and Operational Excellence


Dallas CISO Governing Body
The Governing Body Co-Chairs shape the summit agenda, ensuring that all content is driven By CISOs, For CISOs®.
Governing Body Co-Chairs

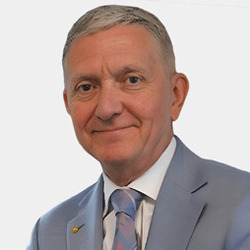
David Bell
CBRE
SVP, CISO

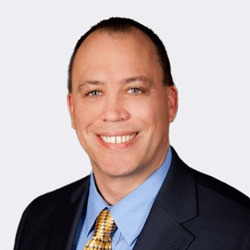
Mustapha Kebbeh
Ultimate Kronos Group
VP & Chief Security Officer

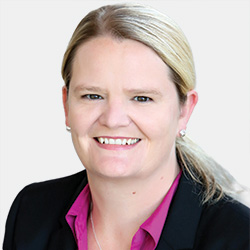
Scott Moser
Sabre Corporation
SVP & CISO

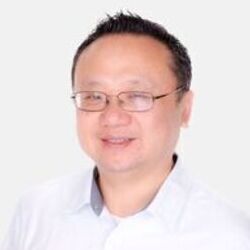
Becky Palmer
National Life Group
VP & CISO
What to Expect at an Executive Summit

Gain New Perspectives from Peers
Hear from CISO practitioners and thought leaders on how they're solving critical challenges impacting your role in Keynote sessions, and participate in smaller, interactive discussions with your peers in Breakout and Boardroom sessions.

Strengthen Your Peer Network
Catch up with familiar faces and build new relationships in your Dallas CISO Community through dedicated networking time in an intimate environment and curated, one-on-one conversations with peers matched based on shared priorities and interests.

Leverage Gartner Insights
Gain data-driven insights and field-tested best practices from a Gartner analyst in the opening Keynote, setting the context for peer conversations throughout the day on the most critical topics affecting your role.
Agenda
8:00am - 8:30am Registration & Breakfast
8:30am - 9:15am Gartner Keynote
Influencing Key Stakeholders
Ethan Budgar
Sr Principal Analyst
Gartner
As cyber risk becomes increasingly tied to business performance, CISOs must drive outcomes through leaders outside the security organization. Success requires more than authority. It depends on building credibility, understanding stakeholder priorities, challenging assumptions, and framing security issues in business terms that inspire action. This session explores practical strategies for influencing decisions, creating urgency, and gaining commitment across the enterprise.
Join this discussion to learn how to:
- Gain commitment for security initiatives from leaders balancing competing business priorities
- Reframe security challenges in business that motivate action and support enterprise risk reduction
- Influence decisions, build urgency, and drive change effectively, even without direct authority
9:15am - 9:40am Networking Break
9:40am - 10:25am Breakout Session
Q-Day Countdown — Preparing for the Quantum Shift
Hosted by Cloudflare
Aaron McAllister
Field CTO
Cloudflare
Post-quantum migration has officially shifted from a theoretical threat to an urgent operational mandate. With finalized NIST standards and pressing regulatory deadlines, CISOs must audit legacy infrastructure, protect long-lived secrets, and hold software vendors accountable — all without disrupting core business operations. This session cuts through the Q-Day hype to deliver a practical, executive-level framework for building cryptographic agility and mitigating supply chain exposure before compliance windows close.
Join this session to explore:
- Mapping high-risk assets, long-lived keys, and vulnerable authentication flows across your ecosystem with targeted asset discovery
- Defining essential PQC readiness criteria for software vendors and third-party partners for supply chain accountability
- Implementing pragmatic strategies to modernize encryption layers for future architectural agility
9:40am - 10:25am Breakout Session
Strengthening Critical Infrastructure Through IT/OT Security Alignment
Hosted by Illumio
Clint Wilson
CISO
HF Sinclair
As operational technology environments become increasingly connected, organizations are facing new cybersecurity challenges that blur the traditional boundaries between IT and OT. At the same time, critical infrastructure operators must balance security, safety, reliability, and regulatory demands while navigating rapid technological change, including the rise of AI and industrial digitization. Effective alignment of people, processes, and technologies helps reduce vulnerabilities, improve operational continuity, and protect mission-critical assets.
Join this session to discuss:
- Shifting of OT security to the CISO
- Aligning IT/OT, culture, risk, and governance
- Building a mature and resilient converged cybersecurity programs
9:40am - 10:25am Executive Boardroom
Reimagining Security Teams — Optimizing AI Agents and Cost
Hosted by Microsoft Corporation
Dd Budiharto
Chief Security Advisor
Microsoft Corporation

Rick Velasquez
CISO
Paradigm
Sonya Wickel
VP, Information Security & CISO
Texas Mutual Insurance Company
As AI agents proliferate in security operations, CISOs must strategically manage token consumption and associated costs, while weighing those costs against the risk they mitigate. Organizational structures are evolving to support agent-centric models, and the hardest questions are as much about people as technology: how roles change, which skills matter, and what new leadership approaches and cross-functional collaboration the shift demands. This session will explore how to balance risk, cost, efficiency and resilience as the enterprise and its workforce adapts to the next wave of AI-driven security.
Join this session to discuss:
- Managing token consumption and aligning FinOps priorities against risk-reduction value
- Redesigning teams, roles and skills for agent-centric security models
- Anticipating future shifts in AI-driven organizational structures and the talent implications
9:40am - 10:25am Executive Boardroom
Securing the Foundation for Trusted AI
Hosted by Concentric AI
Pedro Ferreira
Director of Channel Enablement
Concentric AI

Bryan Chou
Director, Infrastructure & Information Security
Atlantic Aviation
Don Good
CISO
Everest
As organizations accelerate AI adoption, security leaders are being asked to support innovation while maintaining control over sensitive data. Many AI initiatives are revealing longstanding challenges around data visibility, access governance, oversharing, and policy enforcement. The organizations that successfully scale AI will be those that establish trust in the data, controls, and governance frameworks that underpin it.
Join this roundtable to discuss:
- Assessing confidence in AI data visibility and identifying barriers to secure adoption
- Bridging the gap between AI policy and employee behavior, including shadow AI
- Enabling AI innovation while maintaining security without being restrictive
10:25am - 11:10am Networking Break
10:35am - 11:00am Peer-to-Peer Meetings
Peer-to-Peer Meetings
Connect with like-minded peers in a one-on-one setting through Peer-to-Peer Meetings. You will be matched with peers in your community based on your shared interests and priorities.
11:10am - 11:55am Breakout Session
Beyond Generative AI — Preparing for Agentic AI Revolution
Hosted by Cyera

Rick Holland
Data & AI Security Officer
Cyera
The next evolution of artificial intelligence is not simply generating content. It is enabling autonomous systems that can reason, interact with enterprise applications, and execute business processes on behalf of employees and customers. This shift introduces a new category of enterprise risk. AI agents require access to data, applications, systems, and credentials, creating challenges that traditional cybersecurity, identity, and governance models were never designed to address.
This keynote explores:
- Preparing for the Agentic AI era by building a unified approach to data protection, identity security, and AI governance
- Emerging requirements for governing non-human identities, managing AI agent access, protecting sensitive data, and maintaining continuous compliance
- Balancing innovation and risk with a practical framework for visibility
11:10am - 11:55am Breakout Session
Securing Agentic AI Across the Enterprise
Hosted by Island
Jason Trunk
VP & Field CTO
Island
Agentic AI is transforming organizational productivity and revenue but introduces new security and governance challenges. Without traditional onboarding, AI agents can move data unsupervised, use tools maliciously, and create "shadow AI" risks beyond IT’s view. Organizations need a centralized control plane for comprehensive visibility and control across all environments, replacing outdated infrastructure and ensuring secure AI adoption.
Join this session to discover:
- Establishing centralized control for agentic AI
- Managing agentic posture and non-human identities
- Enabling secure governance for safe AI operations
11:10am - 11:55am Executive Boardroom
Securing the Rise of AI Identities
Hosted by Saviynt
David Zacher
Director of Cybersecurity
Atmos Energy
Joe Paul
Senior Director, Cybersecurity Compliance.
WWP Media
According to the International Data Corporation, the number of AI identities is expected to reach 1.3 billion in just two years. Yet many organizations don’t secure AI identities effectively, granting excessive access and relying on outdated, slow processes.
Join this session to learn how to:
- Identify gaps in agent access visibility, ownership, and governance
- Address the unique challenges of identity security in AI environments
- Build scalable identity foundations to enable innovation and efficiency
11:10am - 11:55am Executive Boardroom
Who Gets Access? Identity, Trust, and Control
Hosted by Ping Identity

Loren Russon
SVP of Product & Technology
Ping Identity
Saurin Patel
CISO
Lennar

Leslie Saravia
Director, Security & Compliance
Overhead Door Corporation
As AI agents begin making decisions, accessing systems, and acting on behalf of employees, organizations face a new challenge: balancing trust with control. For CISOs, the question is no longer just who has access, but how to establish accountability, governance, and sovereignty over non-human identities operating across the enterprise. What happens when access is no longer limited to people?
Join this roundtable for a discussion on:
- Using identity to establish trust without sacrificing oversight and sovereignty
- Strengthening security, governance, and accountability as non-human identities scale
- Auditing and governing agent activity through policy, visibility, and oversight
11:55am - 12:30pm Lunch Service







Apply to Participate
Each application is carefully vetted to ensure members meet established criteria, preserving the quality of the network and enabling meaningful, peer‑level discussions among leaders from the world’s leading organizations.
Once you submit your application, a Community Program Manager will schedule a conversation to understand your priorities and interests and complete onboarding, including access to year‑round community events.
Location
Venue & Accommodation
The Westin Irving Convention Center at Las ColinasA block of rooms has been reserved at the The Westin Irving Convention Center at Las Colinas at a reduced conference rate. Reservations should be made online or by calling 972-505-2900. Please mention Gartner CISO Executive Summit to ensure the appropriate room rate.
Deadline to book using the discounted room rate of $369 USD (plus tax) is October 12, 2026.
Your Community Sponsors
Global Thought Leaders

CISO Thought Leaders


Key Sponsors



Program Sponsors



Community Program Manager
For inquiries related to this community, please reach out to your dedicated contact.